| View previous topic :: View next topic |
| Author |
Message |
mibiz1
How do I cheat?
![]() Reputation: 0
Joined: 20 Feb 2008
Posts: 9
|
 Posted: Thu Feb 21, 2008 7:16 am Post subject: results for "Try to find base pointer" |
 |
|
Hi,
Where am I suppose the see the address or result of "Try to find base pointer" scan? In the result list same as result for value scan? I'm trying to cheat on Caesar 4 (v1.1) and having problems locating the pointer levels. I've tried several methods listed below but w/o success.
1) I found the money to be at (example) 0x0727D8F8. Has base+offset of 0x0727D8B8 + 40.
2) This 0x0727D8B8 has 3 other pointer addresses point to it. 0x072BCF14, 0x072BD01C, and 0x072BD04C.
3) The 1st pointer address 0x072BCF14 has 5 other addresses point to it while the other 2 doesn't have any thing pointing to it: 0x18D6BCF4, 0x1A870078, 0x1A870174, 0x1A870234, 0x1A870348.
I did "Pointer scan for this address" for all the addresses mentioned above and got these:
[CaesarIV.exe+0091E318]+1d8
[CaesarIV.exe+0091E324]+a10
[CaesarIV.exe+0091F098]+3bc
[CaesarIV.exe+0091D790]+fc
[CaesarIV.exe+0091E324]+1e4
[CaesarIV.exe+0091E324]+2ec
[CaesarIV.exe+0091E324]+31c
The base pointer [CaesarIV.exe+ code offset(?)] sometimes change but the offset to the memory location always changes when I restart the game or reload the saved game. I've tried pointer scan against all DLLs of the game for those addresses above and got nothing. The DLLS are:
binkw32.dll = movie related?
granny2.dll = RAD game tool
mss32.dll = miles sound system
RomeScripInterfaces.dll = ???
ScriptServer.dll = ???
unicows.dll = MS unicode layer
Apparently the game is coded in ASP.NET v2 since the script DLLs have batch file to register them.
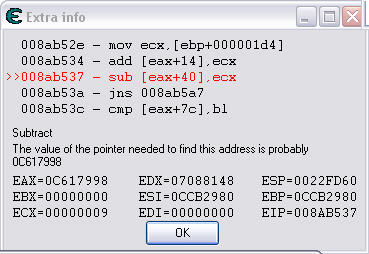
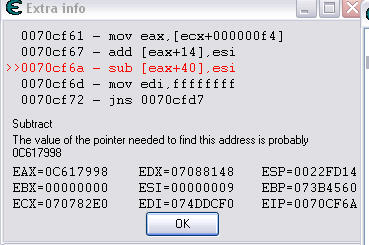
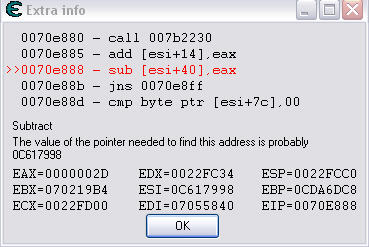
EDIT: added pix of codes accessing that money memory location
| Description: |
|
| Filesize: |
27.26 KB |
| Viewed: |
12326 Time(s) |
|
| Description: |
|
| Filesize: |
25.44 KB |
| Viewed: |
12326 Time(s) |
|
| Description: |
|
| Filesize: |
27.87 KB |
| Viewed: |
12326 Time(s) |
|
|
|
| Back to top |
|
 |
Labyrnth
Moderator
![]() Reputation: 10
Joined: 28 Nov 2006
Posts: 6300
|
| Posted: Thu Feb 21, 2008 9:07 am Post subject: |
|
|
Take 1 of the address's after you find it in debugger like you show images of info button.
View it in memory, then go to the address in lower memory view.
You will see what module you are in.
Whether it is a dll or the games exe.
Now you can use the module name + offset and do an AA script with you assembly.
Also i notice it is changing registers each image as well, but the value leading to the pointer is the same. C617998
You may need to look at altering registers for this.
|
|
| Back to top |
|
|
mibiz1
How do I cheat?
![]() Reputation: 0
Joined: 20 Feb 2008
Posts: 9
|
| Posted: Sun Feb 24, 2008 6:44 am Post subject: |
|
|
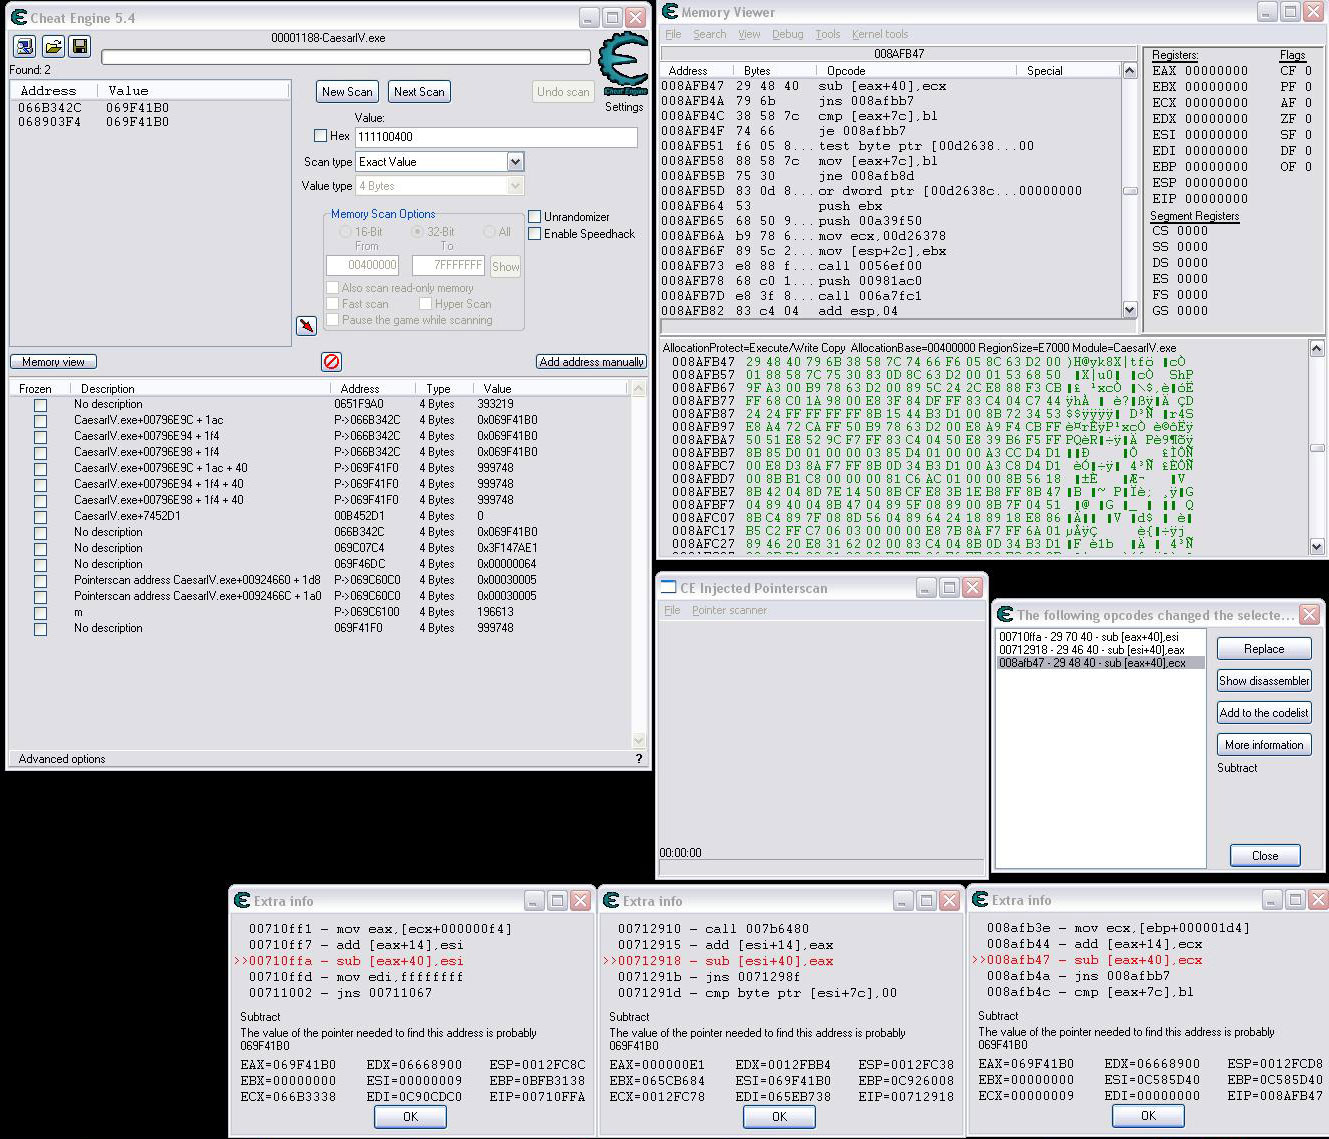
I did what you suggested before posting and thought maybe I've missed something so I tried again, same result. Please see the attachment. In the pix, the money is at 0x069F41F0. The base pointers (2nd level) I've found are:
CaesarIV.exe+00796E9C+1AC
CaesarIV.exe+00796E94+1F4
CaesarIV.exe+00796E98+1F4
If I load a saved game or restart my current scenario, then those addresses are no longer valid. But if the saved game is loaded or a new game starts after the initial launch of CaesarIV.exe, the those pointers are valid... I've tried scanning with Memory Access Exceptions and Use Debug Registers for Code Finder and get the same results.
I didn't have this much problem before with any game before, even Dragon shard was a pain but I've managed to find the locations for all the characters.
Thanks.
| Description: |
|
| Filesize: |
365.75 KB |
| Viewed: |
12293 Time(s) |
|
|
|
| Back to top |
|
|
Labyrnth
Moderator
![]() Reputation: 10
Joined: 28 Nov 2006
Posts: 6300
|
| Posted: Sun Feb 24, 2008 12:29 pm Post subject: |
|
|
See if this works, even after restart.
*If you dont know what it is doing, im just testing to see if the code shift is countered by using the symbol.
It will reverse the instruction and in game instead of decreasing on what your target is, It should increase.
| Code: |
[ENABLE]
CaesarIV.exe+4AFB47:
db 01
[DISABLE]
CaesarIV.exe+4AFB47:
db 29
|
|
|
| Back to top |
|
|
|
 FAQ
 Search
 Memberlist
 Usergroups
 Register
 Profile
 Log in to check your private messages
 Log in


